[ PAVEL MATĚJÍČEK / SPAJK ]

CYBERSECURITY.
IN PLAIN LANGUAGE,
UP TO DATE AND
SO YOU WON’T
FORGET IT.

I show people how attackers think, so they can spot a scam before it’s too late. In training sessions, on stage and on camera.
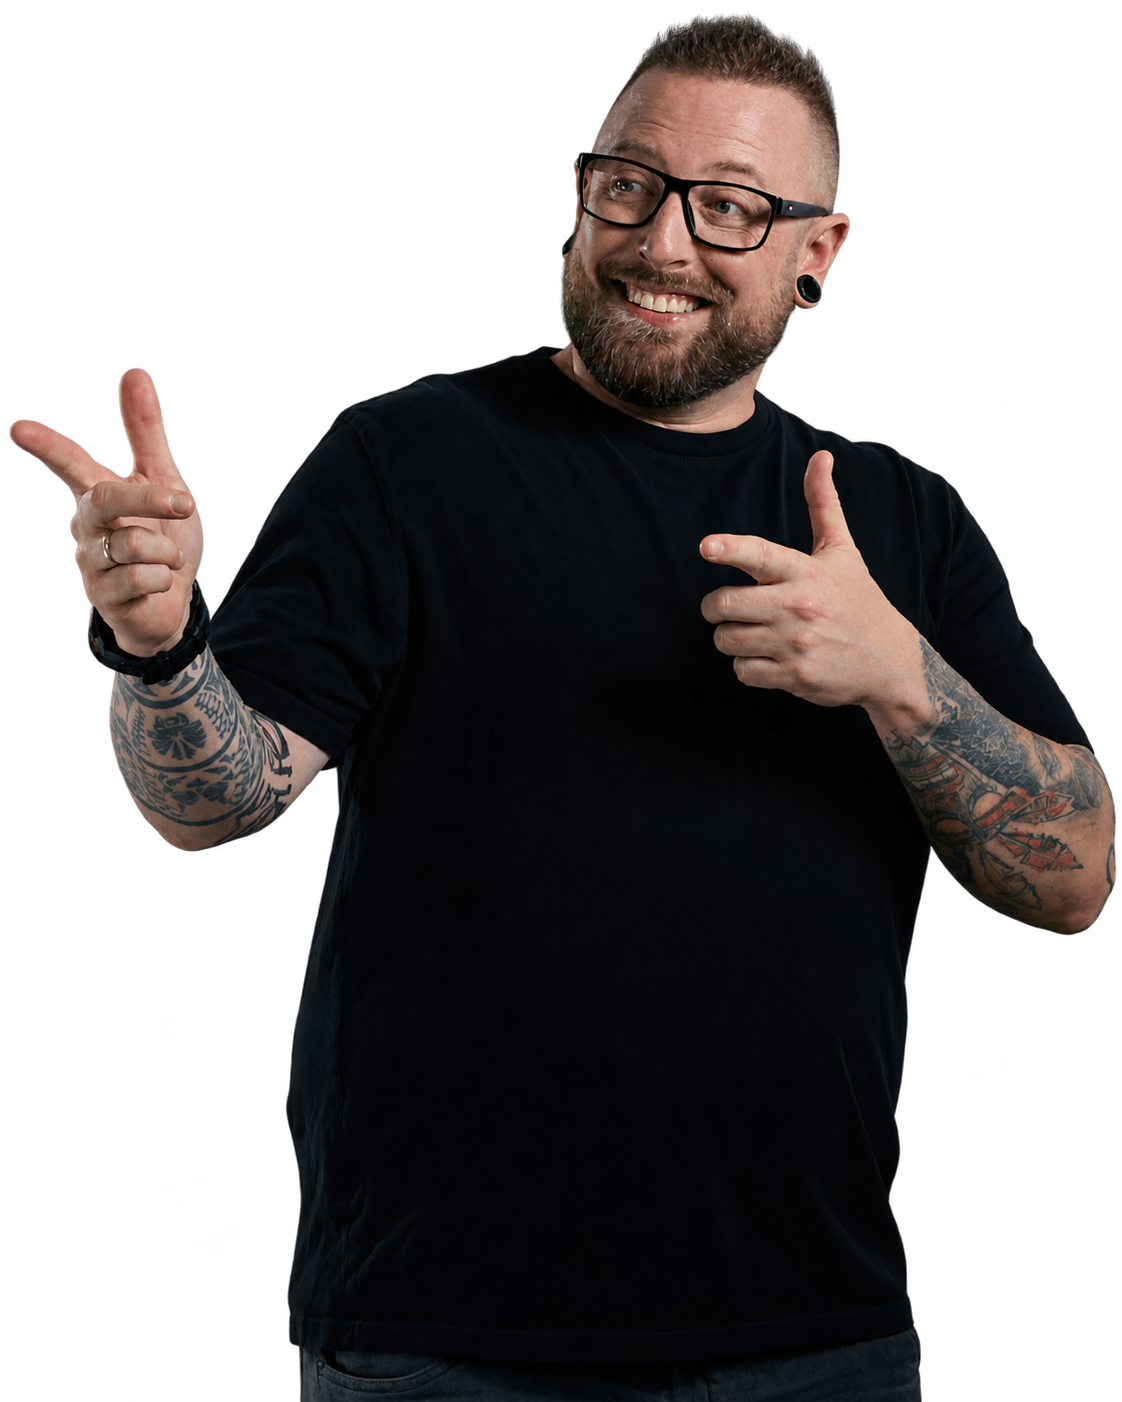
TRAINERETHICAL HACKERBOIT FOUNDER
Pavel Matějíček, Spajk
PAVEL „SPAJK“ MATĚJÍČEKCYBERSECURITY STARTS WITH PEOPLE.
AND IT DOESN’T HAVE TO BE BORING.

LONG-TERM
PARTNERSHIPS

  • O₂
  • Tipsport
  • ČEPS
  • Česká spořitelna
  • Accolade
  • Škoda

01 / WHAT WE CAN CHANGE TOGETHER

I turn employees into
human firewalls.

Real stories. Live demos. Skills you can put to work straight away.

01 / ON YOUR STAGE

Talks that
wake up the room.

Phishing, AI scams, social engineering and the first hour after an incident. For conferences and company events.

Book Spajk for an event ↗
02 / FOR YOUR TEAM

Training that
actually sticks.

From everyday employees to IT teams and management. Content and hands-on demos tailored to the people in the room.

Let’s discuss training ↗
03 / FOR YOUR BUSINESS

Security
put to the test.

With the BOIT team, we test how your people and systems handle real threats. Phishing simulations, OSINT and penetration testing.

Meet BOIT ↗

Choose a training topic ↓

Spajk speaking at CIO Agenda

WHAT PEOPLE SAY

“Pavel is a great speaker who knows how to educate and entertain.”

Daniel Hejda
Ethical hacker · Cyber Rangers

02 / FROM IDEA TO REALITY

What I’m working on
and what I’ve built.

Understand the internet.
And feel safer using it.
These two projects can help.

What else?

Things to read, play and put into practice.
There’s plenty more. And the list keeps growing.Explore all projects ↗

03 / PLAY. LISTEN. UNDERSTAND.

Watch
and listen.

Podcasts, interviews and full-length talks. Pick one and press play. Recordings are in Czech.

Find more videos on my channel.SPAJK’S HACKING ↗

04 / THE PERSON BEHIND THE NICKNAME

From hospitality
to pathology
and ESET.
To the forefront of
cybersecurity education.

My route into IT wasn’t a straight line. I started as a waiter in a French restaurant, then worked as a hospital orderly — from outpatient clinics and operating theatres to pathology. I joined ESET in 2012 and worked my way up from technical support to leading the team.

Today I run BOIT Cyber Security, deliver training, make videos and speak at events. I’m a dad of two boys, a tattooed nerd and a lifelong student of trial and error.

I want ordinary people to understand cybersecurity. Because that’s where security starts.

16,000+
people trainedas of September 2026
2012Joined ESET
2021Went independent
BOITFrom one person to a team

LET’S MAKE IT HAPPEN

Your audience.
My experience.

Planning a conference, training session or interview? Let’s talk about your audience and what you want them to take away.

Choose your training topic10 topics · businesses and schools

Expand a topic to see the content. Then we can tailor it to your audience. Share a link to the whole catalogue or to an individual course.

For businesses

IT security for everyday users3–6 hours

How do you spot a fake email from your boss or a message pushing you to pay via QR code? We’ll look at scammers’ tricks, including deepfakes, and how to protect your phone and accounts with a password manager, MFA and passkeys.

What we cover

  • Password managers, MFA and passkeys
  • Fraudulent business emails, modern phishing, smishing, quishing and recognising attacks beyond email
  • Social engineering, manipulation and the psychology of attackers
  • Deepfakes and AI-powered attacks
  • Mobile device security
  • Practical tips, tricks and recommended tools to strengthen your defences
IT security for management2–4 hours · tabletop option

A cyberattack stops operations. Who makes the decisions, what needs to keep running and what do you tell people? Real incidents will help you work through the choices facing your leadership team.

What we cover

  • Cyber risks from the leadership perspective
  • Management duties and personal accountability in the context of NIS2 and GDPR
  • Security policy and allocation of responsibilities
  • Risk management, business continuity and crisis scenarios
  • Incident communication: internal teams and the media
  • Security investment, priorities and evaluating returns
  • Security culture and employee motivation
  • Practical examples of decisions during incidents
IT security for admins and advanced users6 hours · hands-on workshop

How can an attacker get past a second factor, and what damage can an innocent-looking cable do? See modern phishing, mobile and network attacks in action, then discuss what to check in your own infrastructure.

What we explore

  • Passwords, password attacks, passkeys, 2FA and bypass techniques
  • Modern phishing: email, quishing, smishing and PWA attacks
  • Social engineering and tool demos: Flipper Zero, Rubber Ducky, o.MG, Pineapple…
  • Payment fraud and NFC relay attacks
  • Mobile devices, malware, zero-day scenarios and GrapheneOS
  • IoT, vulnerability scans, VPNs and network security
  • Practical tools and configurations
  • Bonus: PDF handbook for employees and their families
Fraud and vishing: protecting clients and yourself1.5–2.5 hours

Is that really your bank on the phone? Real cases show how scammers earn trust and put people under pressure. Learn how to interrupt a scam and help a client who already has a fraudster on the line.

Attacks in context

  • Fraud in the Czech Republic and its financial impact
  • Organised groups, call centres, forced labour and double scams
  • Examples of attacks and police operations; why scammers target banks

AI defence and the Alenka project

  • AI models for detecting scammers and wasting their time
  • Active threat hunting and disrupting scam portals

Common scam scenarios

  • WhatsApp “Hi Mum…” scams and emergency calls from supposed relatives
  • Fake bankers and “safe accounts”
  • Tech support scams impersonating Microsoft or Apple

The psychology of scams

  • Fear, authority and time pressure
  • Communication dark patterns, defence and prevention

NFC: facts and myths

  • Card-cloning myths and how relay attacks work
  • What clients can actually do

Passwords and documents

  • Demonstrating attacks on weak passwords and common patterns
  • Demonstration of cracking a password-protected PDF
  • Recommended practices, process improvements and Q&A
AI and security3–4 hours

Which parts of a contract can you share with AI, and when should you rewrite the prompt? Everyday work examples show how to protect sensitive data, check answers and set rules people can actually follow.

How AI works

  • Generative models, neural networks and tokens
  • Hallucinations, bias and the limits of AI
  • Tool overview: ChatGPT, Copilot, Gemini, Midjourney…

Effective and safe use

  • Prompting and prompt hygiene
  • Practical business scenarios and safe operating practices
  • Data leaks, unsuitable inputs, public vs enterprise AI
  • Anonymisation and information classification

Company AI policy

  • Rules, roles, data classification and access
  • Prohibited practices and recommended tools

Legal framework and deployment

  • Copyright and the use of AI outputs
  • The AI Act, risk categories and organisational duties
  • Local models and on-premises AI

Current threats

  • Jailbreaks, prompt injection and poisoning
  • Attackers and their AI tools, such as WormGPT
  • AI in phishing, social engineering and ransomware 2.0

Deepfakes and voice cloning

  • Recognising deepfakes and real-world examples
  • Protecting reputation and preventing misuse
Protecting your privacy online3 hours

What can a photo, a social profile or a web search reveal about you? Explore your digital footprint and see which settings and tools help you keep personal and work information under control.

What we cover

  • Private browsers, recommended extensions and alternative search engines
  • Photo and video metadata and how to remove it
  • Mobile devices, social networks and content personalisation
  • Secure communication and end-to-end encrypted messengers
  • Security and encryption tools
  • Understanding IP addresses, DNS, VPNs and Tor
  • Google/Android vs Apple: differences in data protection
  • Alternative operating systems
OSINT: open-source intelligence3–4 days · shorter options by agreement

What can public traces reveal about a company, and how do you know you’ve found the right person? Learn to connect clues from websites, photos and public databases, verify their origins and document your findings in a clear report.

Course content

  • Methodology, ethics, the Czech legal framework and assessing source credibility, reliability and bias
  • Digital identity, anonymity and a safe working environment
  • Tools, frameworks, hardening and sock puppets
  • Footprinting people and organisations; SOCMINT investigation and analysis
  • Visual OSINT (IMINT), EXIF, metadata and reverse image search
  • Advanced search and Google dorking
  • Technical OSINT: domains, DNS, IP addresses and infrastructure
  • Website mapping, TLS certificates and fingerprinting
  • Breach databases, leaks, messengers and searches by email and password
  • The dark web, Tor, marketplaces and cryptocurrency tracing
  • Automation, documentation and graph analysis
  • Writing a professional OSINT report
Ethical hacking fundamentals16 hours · hands-on workshop

How does an attacker get from an online clue to a domain administrator account? Follow the attack step by step in hands-on Azure labs and see where defenders can break the chain.

Trainers: day 1 Pavel Matějíček (CEH, purple team); day 2 Lubomír Ošmera (Microsoft Security Trainer, red teamer).

Day 1: How an attacker gets into a company

  • MITRE ATT&CK in practice
  • Recon: Shodan, Censys, DNSDumpster…
  • OSINT: Maltego, metadata and dorking
  • Social engineering, phishing, quishing and smishing
  • Physical attacks: Flipper Zero, o.MG cable, baiting…
  • Port scanning and gaining access
  • Creating and testing malware in the lab

Day 2: Becoming a domain admin

  • The Active Directory kill chain
  • Enumeration and privilege escalation
  • Lateral movement and persistence
  • Recommended safeguards for your infrastructure

For schools

A day with Klára: what can go wrong online in 24 hours1.5–3 hours · lower and upper secondary

What can happen in just one day on a phone? Follow fourteen-year-old Klára through messages, games and social media, and discuss when to pause, how to handle pressure and whom to ask for help.

What we explore

  • Algorithms, filter bubbles and the influence of social media
  • WhatsApp stalking, channels, location and hidden risks
  • Phishing in Roblox, malware in Minecraft and gaming risks
  • Intimate images, sexting and sharing on Reddit
  • Manipulation, darknet recruitment and fake bankers
  • Interactive demos and discussion
  • Cybersecurity basics: passwords, MFA and digital footprints
Alfy na síti — Gen Alpha onlinemin. 90 minutes · primary grades 1–5

Why does my feed keep showing me similar videos, and what can I do if someone sends me a nasty message? With trainer Tereza Pásková, children explore familiar situations from games and social media and practise responding and asking for help.

Led by Tereza Pásková.

How the programme works

  • Speaking children’s language, without talking down to them
  • A safe, non-judgemental environment
  • Real examples and current trends
  • Active participation, discussion and tips children can use immediately

What children explore

  • Emotions online: how content affects us and what to do when it makes us feel bad
  • Privacy and personal information: what we reveal and what not to share
  • Digital footprints: why “deleted” does not mean gone
  • Reality vs the internet: filters, peer pressure and fake realities
  • Cyberbullying: recognising problems and responding as a target or witness
  • Unsuitable content and manipulation: responding to upsetting content, pressure, ads and clickbait
  • Social media: privacy, sharing and algorithms
  • Security basics: passwords, accounts and shared devices
  • Digital balance: time online and offline
  • Help and support: asking for help is not telling tales
For organisers and media · biography and photo

Pavel Matějíček, known as Spajk, is a trainer, ethical hacker and founder of BOIT Cyber Security. He specialises in social engineering, phishing and cybersecurity education. He spent nearly ten years at ESET. Today, he trains businesses and the public, speaks at conferences, creates the Spajkovo hackování (Spajk’s Hacking) channel and co-hosts the Místo kyberčinu (Cybercrime Scene) podcast for O2 with Honza Dolejš. He explains complex digital threats in a practical, approachable way — with a sense of humour.

Download portrait ↓